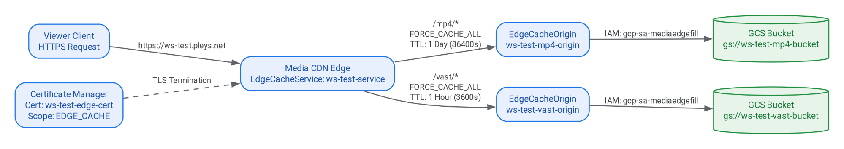
A Media CDN deployment is composed of modular, loosely coupled resources that separate
backend connectivity (EdgeCacheOrigin), client-facing routing and caching
(EdgeCacheService), TLS certificate lifecycle management
(Certificate Manager), and cryptographic access control
(EdgeCacheKeyset). Understanding how these components interact allows you
to update routing rules or swap storage backends independently without disrupting
global edge traffic.
2.1 EdgeCacheService (Services, Routing & CDN Policies)
The EdgeCacheService is the primary client-facing resource in Media CDN.
When you create an EdgeCacheService, Google Cloud allocates dedicated
global Anycast IPv4 and IPv6 addresses at the edge of Google's network. The service
resource is typically managed declaratively via a YAML configuration file
(gcloud edge-cache services import) and governs three layers of request
processing:
-
TLS & Listener Configuration (
edgeSslCertificates,
requireTls): Binds up to five Certificate Manager certificates
(with EDGE_CACHE scope) to terminate HTTPS/HTTP2/HTTP3 (QUIC)
connections at the Google edge PoP closest to the end user.
-
Host & Path Routing (
routing.hostRules and
routing.pathMatchers): Evaluates the incoming HTTP
Host header (such as
ws-test.pleys.net) and dispatches the request to a
named pathMatcher. Inside the pathMatcher, prioritized
routeRules inspect the URL path (via prefixMatch,
fullPathMatch, or pathTemplateMatch), headers, or query
parameters to select the target EdgeCacheOrigin.
-
Route Actions & CDN Policies (
routeAction.cdnPolicy and
routeAction.urlRewrite): Controls how requests and responses
are transformed and cached per route. This includes URL path rewriting
(pathPrefixRewrite), CORS headers, and the cdnPolicy block
which dictates the cacheMode (CACHE_ALL_STATIC,
USE_ORIGIN_HEADERS, FORCE_CACHE_ALL, or
BYPASS_CACHE), Time-To-Live durations (defaultTtl,
maxTtl, clientTtl), and custom
cacheKeyPolicy settings.
2.2 EdgeCacheOrigin (Backend Origins & Failover)
An EdgeCacheOrigin defines an upstream backend server or storage bucket
from which Media CDN fetches content when an edge cache miss occurs (known as an
origin fill). Multiple routes within one or more
EdgeCacheService configurations can reference the same
EdgeCacheOrigin. Key capabilities include:
-
Native Cloud Storage Integration (
gs://): When
originAddress is set to gs://bucket-name, Media CDN
communicates directly with Google Cloud Storage over Google's private backbone using
the Media CDN Service Agent identity.
-
External & Third-Party Origins: Supports standard HTTP/HTTPS
endpoints (such as Live Stream API packagers, GKE ingress, or Compute Engine load
balancers) as well as AWS S3 and Azure Blob Storage buckets (including AWS Signature
Version 4 origin authentication).
-
Resiliency, Timeouts & Failover (
failoverOrigin,
retryConditions, timeout): Each origin can
specify granular timeouts (connectTimeout,
maxAttemptsTimeout, readTimeout), automatic retry
conditions (such as CONNECT_FAILURE, HTTP_5XX,
NOT_FOUND for live streaming segment availability), and a secondary
failoverOrigin resource that automatically serves traffic if the
primary origin experiences an outage.
2.3 Certificate Manager (EDGE_CACHE Certificates & DNS Authorizations)
Media CDN integrates directly with Google Cloud Certificate Manager
(gcloud certificate-manager) to handle SSL/TLS certificates at scale.
Rather than managing standalone certificate resources inside the CDN API, you
provision certificates in Certificate Manager with --scope=EDGE_CACHE so
they are distributed globally across all Media CDN edge locations:
-
DNS Authorizations (
dns-authorizations): Proves
ownership of your domain (for example,
ws-test.pleys.net) using an ACME DNS-01 challenge.
Certificate Manager generates a unique CNAME record that you place in your DNS zone
once, enabling automated certificate issuance and zero-touch renewal without
requiring HTTP port 80 traffic to point to Google Cloud beforehand.
-
Google-Managed Edge Certificates (
certificates):
Provisioned and automatically renewed by Google Certificate Authority once the
linked DNS Authorization is verified. You can also upload self-managed PEM
certificates if your organization mandates custom Certificate Authorities.
2.4 EdgeCacheKeyset (Signed Requests & Token Authentication)
For workloads requiring content protection—such as subscription VOD or pay-per-view
live events—an EdgeCacheKeyset stores the cryptographic keys used by
Media CDN to validate signed URLs, signed cookies, or Dual-Token authentication tokens
at the edge before serving cached bytes:
-
Ed25519 Public Keys: Used for asymmetric URL and cookie signature
verification.
-
Validation Shared Keys (Secret Manager): References HMAC secrets
stored in Google Cloud Secret Manager for symmetric token verification.
2.5 Media CDN Service Agent (Private Origin Authentication)
When you enable and use Media CDN in a project, Google Cloud provisions a dedicated
Google-managed service account known as the Media CDN Service Agent:
service-<PROJECT_NUMBER>@gcp-sa-mediaedgefill.iam.gserviceaccount.com.
By granting this service agent the roles/storage.objectViewer IAM role on
your Cloud Storage buckets (ws-test-mp4-bucket and
ws-test-vast-bucket), Media CDN can fetch objects
privately. You do not need to make your Cloud Storage buckets public
(allUsers) on the internet; all viewer access is strictly funneled
through your Media CDN EdgeCacheService policies.
2.6 Component Summary Matrix
The table below summarizes the core resources involved in our workshop deployment,
their corresponding gcloud CLI command groups, and the specific resource
names we will configure in the upcoming steps.
| Component Resource |
gcloud Command Group |
Workshop Resource Name |
Primary Role in This Lab |
| Cloud Storage Buckets |
gcloud storage buckets |
ws-test-mp4-bucket
ws-test-vast-bucket
|
Private object storage backends storing .mp4 video files and
.xml VAST ad manifests.
|
| Service Agent IAM |
gcloud storage buckets add-iam-policy-binding |
service-<PROJECT_NUMBER>@gcp-sa-mediaedgefill... |
Authenticates Media CDN edge cache fills against private GCS buckets via
roles/storage.objectViewer.
|
| DNS Authorization |
gcloud certificate-manager dns-authorizations |
ws-test-dns-auth |
Generates the ACME CNAME challenge record to prove ownership of
ws-test.pleys.net.
|
| Edge SSL Certificate |
gcloud certificate-manager certificates |
ws-test-edge-cert |
Google-managed TLS certificate (--scope=EDGE_CACHE) terminating
HTTPS traffic for ws-test.pleys.net.
|
| EdgeCacheOrigin |
gcloud edge-cache origins |
ws-test-mp4-origin
ws-test-vast-origin
|
Maps Media CDN origin definitions to
gs://ws-test-mp4-bucket and
gs://ws-test-vast-bucket.
|
| EdgeCacheService |
gcloud edge-cache services |
ws-test-service |
Binds ws-test.pleys.net, attaches
ws-test-edge-cert, and routes /mp4 (1d TTL) and
/vast (1h TTL) with FORCE_CACHE_ALL.
|
Understanding how FORCE_CACHE_ALL interacts with Private Cloud Storage
origins is critical for this workshop. When Media CDN fetches an object from a private
GCS bucket using its Service Agent, Cloud Storage automatically attaches a
Cache-Control: private, max-age=0 header to the HTTP response because the
request was authenticated. Under USE_ORIGIN_HEADERS or
CACHE_ALL_STATIC, Media CDN would honor the private
directive and refuse to cache the asset. Setting
cacheMode: FORCE_CACHE_ALL instructs Media CDN to override origin
Cache-Control headers and unconditionally cache every successful
200 OK / 206 Partial Content response for the duration
specified in defaultTtl (86400s for /mp4 and
3600s for /vast).